FusionAuth
    • Home
    • Categories
    • Recent
    • Popular
    • Pricing
    • Contact us
    • Docs
    • Login
    1. Home
    2. dan
    3. Posts
    • Profile
    • Following 0
    • Followers 10
    • Topics 690
    • Posts 2,746
    • Best 172
    • Controversial 0
    • Groups 4

    Posts made by dan

    • RE: Sending an “inactive account, will be marked dormant” email in FusionAuth

      Not as a single feature, but doable with some glue code. FusionAuth has no built-in “inactivity warning” workflow or scheduler for this.

      It does give you the pieces: a lastLoginInstant on every user, a user search API, an email send API, and user deactivation. You wire them together with a small scheduled job (cron, Lambda, GitHub Action, etc.) outside FusionAuth.

      Set up a daily job that does three things:

      • Finds users whose last activity was about 55 days ago and who haven’t been warned yet.
      • Sends them the warning email and records that you did.
      • Finds users who are 60+ days inactive and marks them dormant.

      If a user logs in during the 5-day window, their lastLoginInstant updates and they drop out of the step 3 query automatically.

      Use the User Search API with an Elasticsearch/OpenSearch query on lastLoginInstant (milliseconds since epoch). This needs the Elasticsearch/OpenSearch search engine. The database search engine doesn’t support range queries on this field.

      POST /api/user/search
      {
        "search": {
          "numberOfResults": 500,
          "query": "{\"bool\":{\"must\":[{\"range\":{\"lastLoginInstant\":{\"lt\":1760000000000}}}],\"must_not\":[{\"term\":{\"data.dormantWarningSent\":true}}]}}"
        }
      }
      

      Compute the lt value in your job as now - 55 days (so replace 1760000000000). Users who have never logged in won’t have a lastLoginInstant, so decide whether to fall back to insertInstant for them.

      You can use FusionAuth to send the email or your own system. If you choose the former, create an email template in Customizations → Email Templates, then call the Send Email API with the matching user IDs:

      POST /api/email/send/{emailTemplateId}
      {
        "userIds": ["<id1>", "<id2>"],
        "requestData": {
          "daysInactive": 55,
          "daysUntilDormant": 5
        }
      }
      

      Your template body can then use FreeMarker:

      Hi ${user.firstName!"there"},
      
      As part of our routine account security measures, we monitor accounts for
      inactivity. We haven't detected activity on your account in the last
      ${daysInactive} days, and it is scheduled to be marked dormant in
      ${daysUntilDormant} days unless activity is detected.
      
      Log in to keep your account active: https://login.example.com
      

      requestData values are available at the top level of the template, so you can reuse the template if you change the thresholds later.

      After a successful send, patch the user to record that they've been notified so you don't send them multiple emails:

      PATCH /api/user/{userId}
      {
        "user": { "data": { "dormantWarningSent": true, "dormantWarningSentAt": 1760000000000 } }
      }
      

      The must_not clause in the search query above then skips them. If the user logs in, clear the flag so they can be warned again in the future. A user.login.success webhook receiver that uses the API is a clean place to do that.

      As far as what you actually do when the user is marked dormant, you have two options:

      • Deactivate the user. DELETE /api/user/{id} (soft delete) sets active=false, which blocks login. To reactivate, call PUT /api/user/{id}?reactivate=true. Deactivation also fires a user.deactivate event that you can consume via webhook to notify downstream systems.
      • Flag only. Set user.data.dormant = true and handle it in your app where you might do a step-up or force an account recovery. This is gentler and keeps the account usable after a step-up.

      For a true “close the account” outcome, deactivate first. Hard-delete (?hardDelete=true) only after a retention period that satisfies your compliance requirements.

      Caveats:

      lastLoginInstant updates when a user authenticates. Silent token refreshes using an existing refresh token don’t necessarily count as logins, so a user with a long-lived session in your app could look inactive. If that matters, track your own activity timestamp in user.data (updated by your app or a webhook) and query that instead. Test this against your own setup before relying on it.

      user.lastLoginInstant is global to the user within a tenant. Each registration also has its own lastLoginInstant (user.registrations[].lastLoginInstant). If “inactive” should mean inactive in a specific application, query on that field and filter by applicationId.

      Run the job daily and use a window, not an exact day match, so a missed run doesn’t skip anyone.

      Page through search results (startRow) rather than assuming one page covers everyone.

      Test with a user whose lastLoginInstant you’ve backdated in a non-production tenant.

      Make sure your Send Email API key has only the endpoints it needs (search, send email, patch user, deactivate).
      posted in Q&A
      danD
      dan
    • Sending an “inactive account, will be marked dormant” email in FusionAuth

      I want to email users after 55 days of inactivity, warn them they’ll be marked dormant in 5 days, and then mark them dormant.

      Does FusionAuth do this out of the box?

      posted in Q&A email dormant account warning
      danD
      dan
    • RE: Data analysis of login/user data from FusionAuth

      You want to use FusionAuth webhooks to push data into your pipelines. I imagine the JSON will differ, so you might need to modify your mapping layer, but we should be able to provide the data you expect.

      Here's our general webhook documentation.

      Some events you might be interested in:

      • User login success which includes the authentication method
      • User login failure
      • Two factor method added
      • User create

      Where possible, avoid transactional webhooks because you're using this for analytics and transactional webhooks impact workflow duration negatively.

      You can also use the Search API to get adhoc counts/true things up, but it won't necessarily have the richness of data of the webhooks.

      posted in Q&A
      danD
      dan
    • Data analysis of login/user data from FusionAuth

      Our data team has enjoyed lots of data points and insights from our existing auth solution. Specifically around users, data like:

      • sign in type (Apple login, Google login, phone number, emails)
      • MFA enabled/disabled
      • what kind of MFA
      • registration info

      We have data pipelines set up to ingest and turn this data into meaningful insights for the business.

      We want to make sure we maintain these important insights. How can we do this?

      posted in Q&A insights analytics login flow
      danD
      dan
    • RE: lastLoginInstant data lost during upgrade from 1.57.0 to 1.59.1

      Hiya @florent-bossuyt ,

      Thanks for using FusionAuth.

      The upgrade to 1.59.0 added support for phone number as a first class identity. While I don't know for sure, it is possible that impacted lastLoginInstant. I'm not aware of any bug filed.

      It's also possible you can find the data previously in the lastLoginInstant in the user.identities[x].lastLoginInstant value, available when you retrieve a user.

      Since this is not a known issue, there's no documented procedure for reconciling the data, unfortunately.

      Here's one approach, though.

      If you have a database backup of the 1.57.0 release, you could stand up a FusionAuth instance pointing to that, and find all the users with a lastLoginInstant that is not null (set A). You'd then run the same query against your prod instance (set B). Then find the folks in set A who are not in set B (call them set C). Set C are the people you need to update.

      Unfortunately, you can't update their lastLoginInstant directly. But you can fake a login using the passwordless APIs, which should set it. That is outlined here.

      So you'd want to perform that for all the users in set C.

      Hope that helps.

      posted in Q&A
      danD
      dan
    • RE: Creating User without Password

      As of version 1.59.0, you can create users without passwords.

      posted in Q&A
      danD
      dan
    • RE: Additional authentication assurance without using step-up MFA

      You can use the linked APIs, and that’s the option most people find first. The step-up flow in the API docs works, but means your app owns the challenge. It has to start it, collect the code, and handle the result. That’s a lot for what is basically “make the user log in again because they are about to do a sensitive thing.”

      There’s another way that’s a little different, and it leverages login. Since version 1.60 the authorize endpoint supports the standard OIDC prompt and max_age parameters.

      When your app hits a sensitive action, don't call any specific APIs. Instead, it can redirect the user to /oauth2/authorize with prompt=login and/or with a max_age small enough that their existing SSO session doesn’t satisfy it. FusionAuth shows the hosted login page, the user authenticates, and you get a fresh token back. Same code you already wrote for login, with one query parameter added.

      Make sure you put the current page/location in the state so you can deliver the customer back to where they were. Here's a video on deep linking.

      Using either max_age=0 and prompt=login end up in roughly the same place. I’d use max_age if you want a window like “re-auth if it’s been more than five minutes,” and prompt=login if you want it every time.

      A successful redirect doesn’t prove everything. Your app still has to decide whether the token it’s looking at came from a recent authentication.

      That’s what the auth_time claim is for. It’s a reserved claim in the JWT body (it moved there in 1.60, and lambdas can’t override it), so your resource server compares it against the clock and rejects beyond your threshold. If it’s too old, send the user back through authorize.

      That’s basically the max_age half of RFC 9470, just without FusionAuth issuing the WWW-Authenticate challenge for you. You’d write that 401 yourself.

      Caveats:.

      • This forces a re-login, not necessarily a stronger one. If the user re-authenticates with a password and nothing else, you’ve proven recency and nothing about strength. If you need the second factor on that re-auth, you need MFA to actually fire. A static policy of Required will do it. On Enterprise, the MFA Requirement Lambda can make the decision per request.
      • There’s no acr-style “this was step-up” claim. You get “authenticated at time T,” not “authenticated with a second factor at time T.” If your auditors need the latter, this approach won’t give it to you cleanly, and falling back to the step-up auth API is a better option.
      • It’s a full redirect. For a banking-style “confirm this transfer” flow where bouncing the user to another page is a non-starter, the step-up API approach is still right.
      • This only works when you are using the hosted login pages, not the Login API.

      The short version: if sensitive actions are coarse-grained (“view the billing page,” “change the email address”), the redirect approach might work for you. It’s less code, the hosted pages handle the UI, and you’re not maintaining a custom MFA challenge.

      But if you need per-operation binding or proof of which factor was used, look at the step-up API.

      posted in Q&A
      danD
      dan
    • Additional authentication assurance without using step-up MFA

      I need the user to prove they’re still the user before a sensitive action. Do I really have to wire up the Two-Factor APIs to use step-up MFA auth to do that?

      posted in Q&A step-up mfa auth
      danD
      dan
    • RE: Adding a 'sign up or login CTA' to your pages for unauthenticated users

      This is going to vary based on your publishing system, but you can use FusionAuth's OIDC prompt=none to see if users have an active SSO session.

      If the user has checked remember me and has logged in within the tenant session timeout, the request will succeed, otherwise it will fail.

      Step 1: Main Page

      This creates the iframe and listens for the result.

      On your main page, create the hidden iframe targeting FusionAuth with prompt=none. You also listen for a message event from the iframe to know whether to display or hide the CTA <div>, which needs the id trial-cta:

      // 1. Listen for the result sent back from the iframe callback page
      window.addEventListener('message', (event) => {
        // Verify the origin matches your application domain for security
        if (event.origin !== window.location.origin) {
          return;
        }
      
        const ctaDiv = document.getElementById('trial-cta');
      
        if (event.data && event.data.type === 'SILENT_AUTH_RESPONSE') {
          if (event.data.status === 'authenticated') {
            // User has an active SSO session; keep CTA hidden
            if (ctaDiv) {
              ctaDiv.style.display = 'none';
            }
          } else if (event.data.status === 'login_required') {
            // User is not authenticated; show the trial CTA popup/div
            if (ctaDiv) {
              ctaDiv.style.display = 'block';
            }
          }
        }
      });
      
      // 2. Create the hidden iframe to initiate the prompt=none request
      const iframe = document.createElement('iframe');
      iframe.style.display = 'none';
      iframe.src = 'https://<your-fusionauth-instance>/oauth2/authorize?' +
        'client_id=<YOUR_CLIENT_ID>&' +
        'response_type=code&' +
        'redirect_uri=https://<your-app-domain>/silent-callback.html&' +
        'scope=openid&' +
        'prompt=none&' +
        'state=<YOUR_STATE>';
      
      document.body.appendChild(iframe);
      

      Step 2: Callback Page

      Configure this page as an authorized redirect URI in your FusionAuth application [Request Parameters].

      When FusionAuth redirects back with the authorization code code or error=login_required, this page parses the URL and communicates back to the parent window:

      // Parse query parameters from the redirect URI
      const params = new URLSearchParams(window.location.search);
      const code = params.get('code');
      const error = params.get('error');
      
      if (code) {
        // Session exists: notify the parent window
        window.parent.postMessage({
          type: 'SILENT_AUTH_RESPONSE',
          status: 'authenticated',
          code: code
        }, window.location.origin);
      } else if (error === 'login_required') {
        // No active session: notify the parent window to show CTA
        window.parent.postMessage({
          type: 'SILENT_AUTH_RESPONSE',
          status: 'login_required'
        }, window.location.origin);
      }
      

      Cautions And Additional Considerations

      This won't work across all browsers, especially those with privacy features or if your FusionAuth instance isn't on the same root domain as the application. More details here.

      Test the scenarios you need to support.

      The CTA should include information about how to sign up or log in if the user already has an account.

      You may want to add server or client side logic to obfuscate the page contents.

      posted in Q&A
      danD
      dan
    • Adding a 'sign up or login CTA' to your pages for unauthenticated users

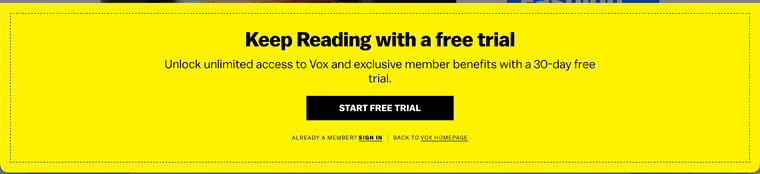
      How can I add a CTA to get users to log in to my news site, like this one from vox?

      Screenshot 2026-10-03 at 6.37.05 AM.png

      posted in Q&A cta paywall login
      danD
      dan
    • RE: Slack-style multi-tenant login: resolve the tenant, then send (or fake) a passwordless code

      Both entry points, and especially the anti-enumeration behavior on the known-tenant path, are best built by calling FusionAuth's passwordless APIs directly from your own UI rather than relying on the hosted login pages. Here's more on the difference.

      Using the API is the only way to get full control over what the UI shows on a failure.

      Known-tenant entry (acme.ourapp.com)

      • Maintain your own slug/domain → tenantId table (outside FusionAuth), populated when you provision each tenant via the Tenant API. FusionAuth has no built-in hostname-to-tenant mapping. You can learn more in the multi-tenant guide.
      • At request time, resolve the subdomain to a tenantId from that table (outside FusionAuth). If nothing matches, show "Workspace not found" — this never touches FusionAuth.
      • Build your own "enter your email" screen for this workspace (not FusionAuth's hosted page — you need to control what's shown on failure, which the hosted page won't let you do).
      • When the user submits an email, your backend calls /api/passwordless/start with that tenantId + your Universal Application id + the email as loginId. Universal Application docs here.
      • Branch on the response, entirely inside your backend:
        • 200, code sent → hang onto the returned code value, respond to your frontend with a generic "we sent you a code" message, and show your own "enter the code" screen.
        • 404, no user found → this is the real signal Slack is hiding. FusionAuth returns a 404 with an empty body when no user matches the tenant. Instead of surfacing that: send your own "no account with this email in this workspace" notice through your own transactional email provider (outside FusionAuth or using the send email API), then respond to your frontend with the exact same "we sent you a code" message. Show the identical "enter the code" screen either way.
      • Completing the challenge:
        • Real branch: verify the code the user types via /api/passwordless/login (tenantId + code), which returns tokens; pair this with the Hosted Backend / BFF if it's a SPA. Alternatively, redirect the browser to /oauth2/passwordless/{code}?tenantId=<tenantId>&client_id=<id> and let FusionAuth's hosted page take over the code-entry step. This is the URL FusionAuth's own passwordless email template constructs for the "click to log in" link, so redirecting there yourself just skips the email round-trip.
        • Fake branch: there is no FusionAuth code to hand off, so there's nothing to redirect to on FusionAuth's hosted domain — you have to own the "enter code" screen yourself here. Whatever the user types, respond with the same generic "invalid or expired code" error you'd give a real wrong code; never a distinct message. If you're using the hosted-page redirect for the real branch, don't try to fake that redirect for this branch — just render your own equivalent screen and always reject, rather than attempting a look-alike hosted destination.
        • Pad the fake branch's response time to roughly match a real Start call, so the two paths don't diverge on timing, which would leak the same thing you're hiding in the UI.

      Generic entry (ourapp.com/login)

      • Call /api/user/search with a global (not tenant-scoped) API key and no tenantId filter, searching by the submitted email. Each matching User record already includes its own tenantId, so this single call tells you every workspace the email belongs to. This pattern (global key, /api/user/search?queryString=<email>, results include per-tenant matches) is answered on the forum. Keep the key server-side only.
        • If you'd rather not run a global-key search on every anonymous request (latency, or wanting the key confined to a webhook receiver instead of a public endpoint), you can maintain your own email → tenantId[] table fed by FusionAuth's user.create / user.update / user.delete webhooks instead. Docs at https://fusionauth.io/docs/extend/events-and-webhooks/. Either is fine — this is a trade-off, not a hard requirement.
      • Branch on the result (outside FusionAuth):
        • No match → "No account found," stop there.
        • One match → continue with that tenant.
        • Multiple matches → show a workspace picker, then continue with the chosen one. This is currently functionality you have to build yourself, though there is an open issue.
      • Once a tenant is resolved, it's the same steps as section 1 from "build your own enter-email screen" onward — including the fake-challenge branch, if you want the same anti-enumeration behavior here too (Slack's generic "find your workspaces" entry also avoids confirming or denying a match directly, for the same reason).

      A few things worth flagging

      • FusionAuth users are tenant-scoped records — the same person needs a separate User object per workspace they belong to.
      • API key scope matters: the cross-tenant search in section 2 needs a global key; the tenant-specific calls in section 1 can safely use a tenant-scoped key. [Docs](Docs at https://fusionauth.io/docs/apis/api-keys).
      • The SSO session cookie isn't tenant-aware across hostnames — FusionAuth doesn't currently support true multi-tenant SSO through the hosted pages, so the user behavior when switching tenants requires another login. Always pass tenantId explicitly on every call.
      • Passwordless API reference for the exact Start/Login request and response shapes:
      posted in Q&A
      danD
      dan
    • Slack-style multi-tenant login: resolve the tenant, then send (or fake) a passwordless code

      We're building a multi-tenant app where each customer is a FusionAuth tenant, similar to how Slack has one "workspace" per customer. We'd like two entry points, like Slack has:

      • A known-tenant URL (acme.ourapp.com) that takes returning users straight to their workspace's login.
      • A generic entry point (ourapp.com/login) where someone just types an email — if it doesn't match any tenant, show "No account found"; if it does, send them a one-time code.

      We'd also like to match Slack's exact behavior on the known-tenant URL: even if the email typed in isn't a member of that workspace, still show the same "enter your code" challenge screen. The "no account" information should only ever reach the person by email, never through the UI — that's what lets someone try a few email addresses if they forget which one they used for a given workspace.

      What's the current best practice for doing this with FusionAuth?

      posted in Q&A slack magic link multi-tenant
      danD
      dan
    • Seeking product feedback on FusionAuth's logging

      FusionAuth's logging isn't one system, it's three: system/app logs on disk or stdout (monitor docs, troubleshooting), audit logs for admin UI changes via webhooks or the Audit Log API, and event logs for debugging surfaced through webhooks or the Event Log API.

      None of them ship anywhere on their own, so if you want this in Datadog or Splunk, you're polling the API or writing your own ingester (by following doc, but still).

      We're looking for feedback on this.

      What's great about FusionAuth's logging, and what sucks or needs to be improved?

      posted in Announcements
      danD
      dan
    • RE: What are the use cases for the user.data.email field?

      It is useful in a few scenarios.

      • When you have users that share an email address, but are in the same tenant and have distinct accounts. FusionAuth enforces uniqueness on user.email per-tenant.
      • When your users have a username (such as an account number) as a main unique identifier, but need self-service account recovery.
      • When you have duplicate email addresses in a legacy system and are migrating them to FusionAuth, whether they point to the same account or not. You can move the users over and address email updates or account merges later.

      Not all email related functionality is available when using user.data.email, but common workflows like forgot password are.

      posted in Q&A
      danD
      dan
    • What are the use cases for the user.data.email field?

      I see the user.data.email field is used when it is present and user.email is not present. From the doc:

      This field will be used as the email address if no user.email field is found. This field may be modified by advanced registration forms or the API. Setting this value to another account's email address allows that account to, in some cases, access information about this user.

      What are the use cases for that field?

      posted in Q&A
      danD
      dan
    • RE: What are FusionAuth entities good for?

      Entities are one of the most flexible parts of FusionAuth and can be used to represent links and/or permissions between domain objects and users.

      Entity types are like classes in an object-oriented programming language, which define the permissions that an entity can have.

      Entities are similar to objects, in that they are an instantiation of an entity type. No behavior though, and no inheritance.

      Entities are connected to users and other entities via grants. You can think of this setting up a directed permission graph that can be traced.

      0 to N permissions are attached to each grant.

      There are three major uses for entities:

      • the client credentials grant (agentic, machine to machine or service account authentication)
      • building limited fine grain authentication (FGA-ish) systems that don't need full ReBAC, but do want to use a permission graph or dynamically add and remove permissions
      • modelling permissions on something you don't log into

      A few notes about entities:

      • you'll want to get familiar with the API or the client libraries; entities are managed in code. Both in creating the graph and reading it from your application.
      • each entity has a data field which can handle arbitrary JSON and is searchable
      • the graph can be cyclic if you make bidirectional grants between entities. Users cannot accept grants, they can only be granted permissions to entities.
      • if you need full ReBAC or ABAC, you want FusionAuth FGA. More functionality, including automatic relationship graph traversal. The downside is you have to sync data and run a separate service.
      posted in Q&A
      danD
      dan
    • What are FusionAuth entities good for?

      I'm curious about entities. What are they good for?

      posted in Q&A entities
      danD
      dan
    • RE: Importing users over time

      As of 1.69.0, you can now update the password hash using the User API.

      From the documentation, the passwordFieldType is the API field to use. This field:

      Describes what user.password in the request is. The possible values are:

      HASHED - user.password is an already hashed value. When this value is supplied, user.encryptionScheme, user.factor, user.password, and user.salt are required.
      PLAINTEXT - user.password is a plain text/unhashed value. FusionAuth will hash this value according to user.encryptionScheme and user.factor.

      posted in Q&A
      danD
      dan
    • RE: Email MFA Timeout

      You want to modify the Two-Factor Login duration in the Tenant Settings, which applies across to SMS and MFA methods.

      https://fusionauth.io/docs/get-started/core-concepts/tenants#advanced has more details.

      posted in Q&A
      danD
      dan
    • Email MFA Timeout

      Users who's email is lagged by 30 - 60 seconds , the emailed MFA verification code has expired by the time they receive them. I've done a Zoom meeting with the user and verified they are doing everything correctly, but their email is web mail based and must be from cloud provider that has a really slow system. They probably get the email about 60 seconds of they click send verification code and it always fails to verify.

      I can't find anything in settings to change the timeout or searching the documentation. Is there a setting for this somewhere that I could change or could Emailed Verification codes be good for at least 90 seconds?

      ported to forum from https://github.com/FusionAuth/fusionauth-issues/issues/3545

      posted in Q&A mfa email timeout
      danD
      dan